Wasabi offers Single Sign-On (SSO) functionality for Wasabi accounts using the JumpCloud (identity provider) system, based on SAML2 (Security Assertion Markup Language) integration.
This article provides configuration instructions for both the IdP administrator and the SSO user to properly configure and complete a Wasabi Console login using your organization's JumpCloud SSO service.
Configuring SAML App in JumpCloud (IdP Side)
Log in to JumpCloud (https://jumpcloud.com) as an Administrator.
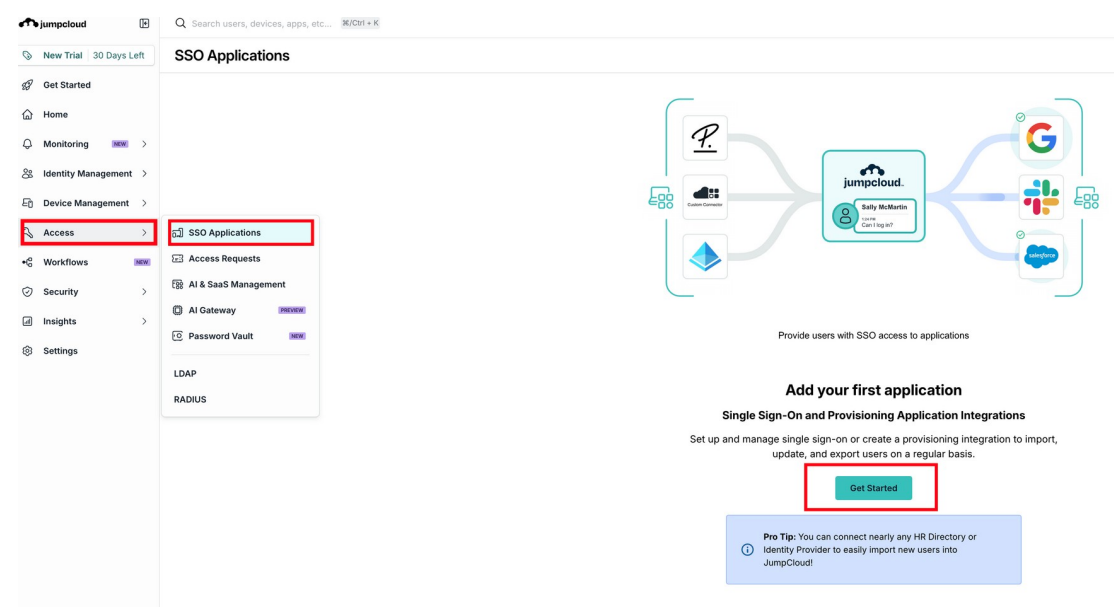
Select Access from the navigation menu, then select SSO Applications, and click Get Started or Add New Application. The Create New Application Integration page is displayed.
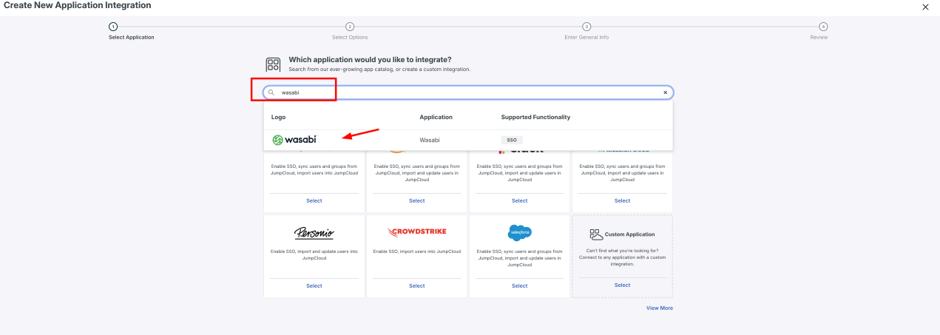
In the Search field, type Wasabi, then click Next at the bottom of the page. The Display Label panel is displayed.
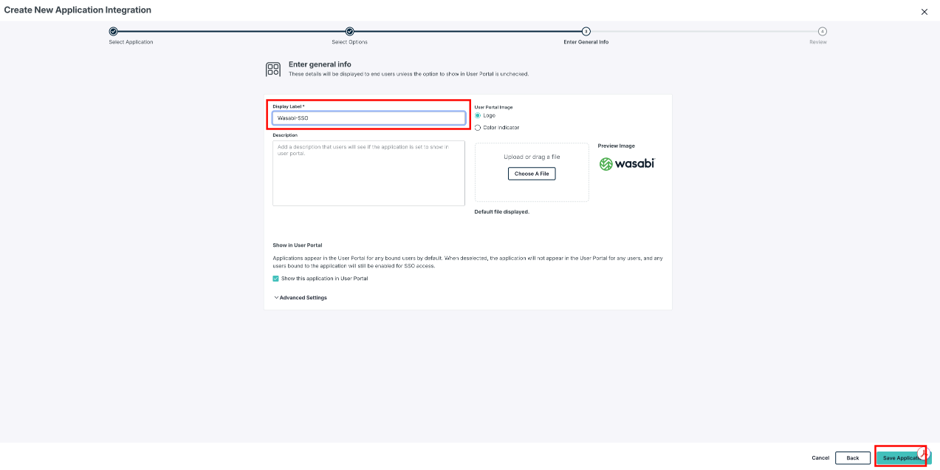
In the Display Label box, type Wasabi-SSO, for example, then click Save Application. On the next page, click Configure Application at the bottom right. The SSO page is displayed.
On the SSO page, configure the SAML connection settings that JumpCloud uses to communicate with Wasabi for SSO authentication.
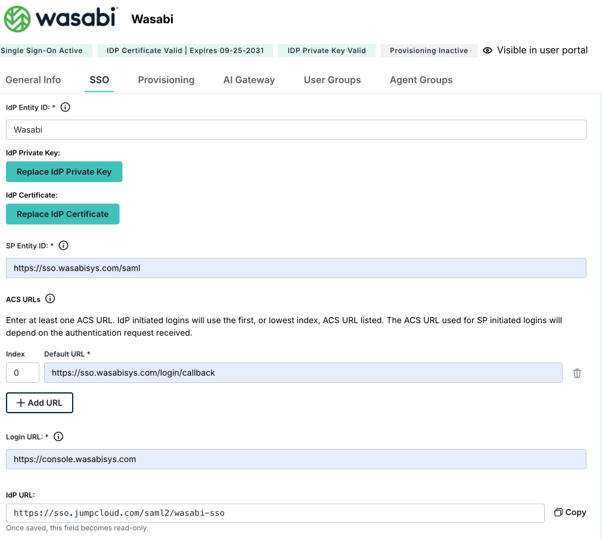
Use the following settings:
IdP Entity ID—Type Wasabi. The IdP entity ID is the unique, case-sensitive identifier that JumpCloud uses for this service provider. Be sure that the value you enter matches the Identity Provider entity ID you configured on the Wasabi Console SSO configuration page.
SP Entity ID — Use the URL:
https://sso.wasabisys.com/samlACS URLs—Use the URL:
https://sso.wasabisys.com/login/callbackLogin URL—Use the Wasabi Console URL:
https://console.wasabisys.comIdP URL—Keep this URL.
Scroll down to the Attributes section, then click Attribute to configure the user and group attributes that JumpCloud sends to Wasabi in the SAML assertion.
In the User Attributes section, click Add Attribute.
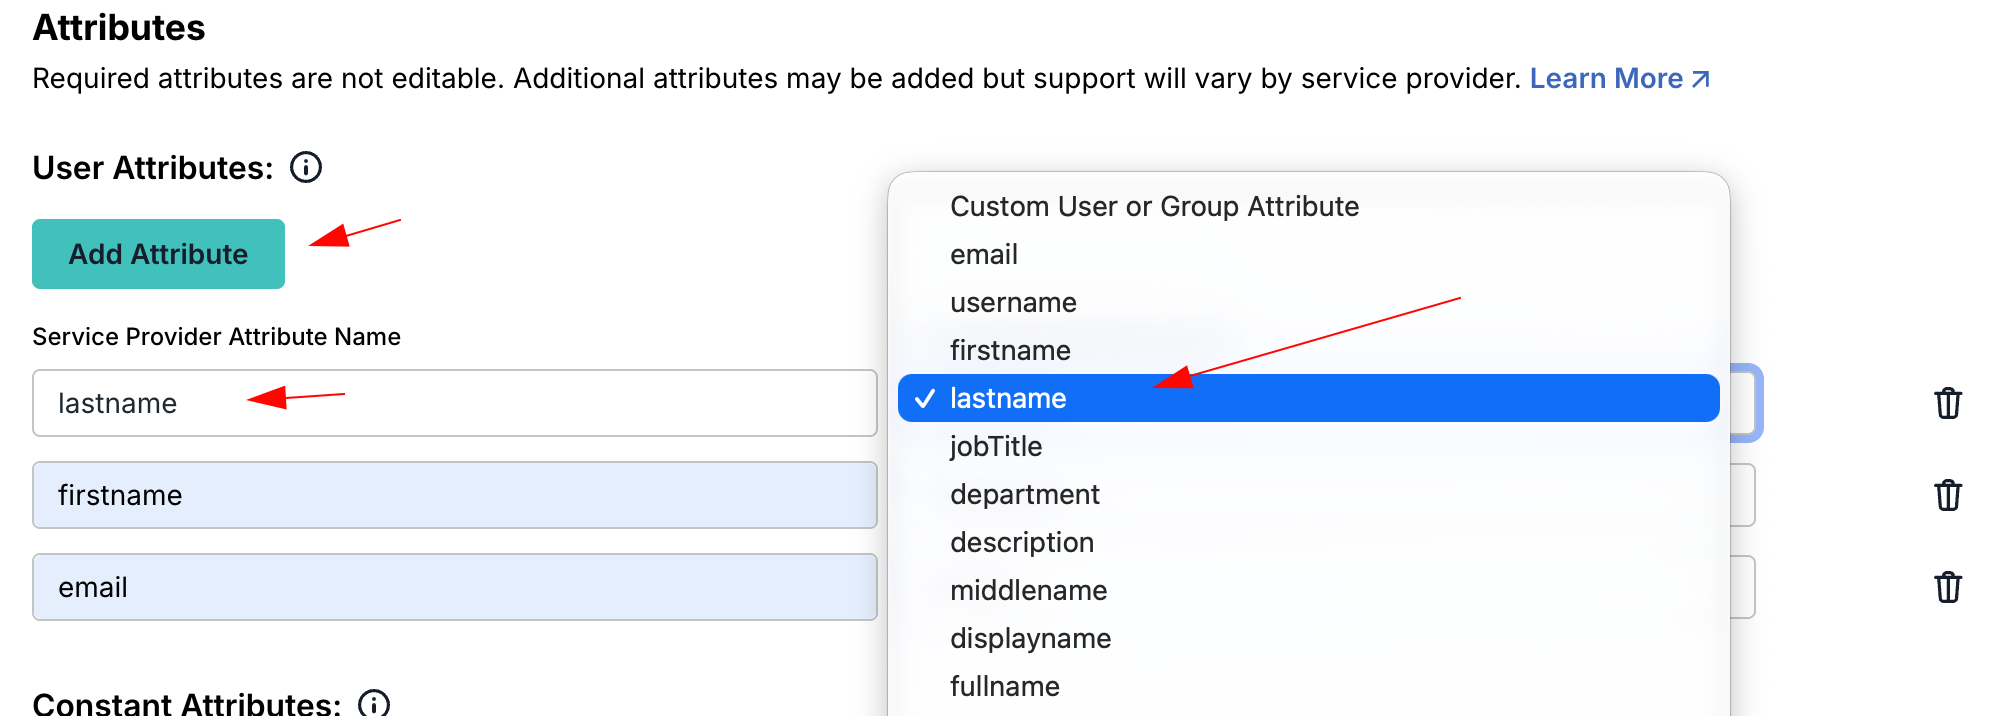
Under the User Attributes, map the following attributes:
Service Provider Attribute Name—Type the attributes: lastname, firstname, and email in the corresponding fields.
JumpCloud Attribute Name—Select the same attributes from the dropdown menus: lastname, firstname, and email.
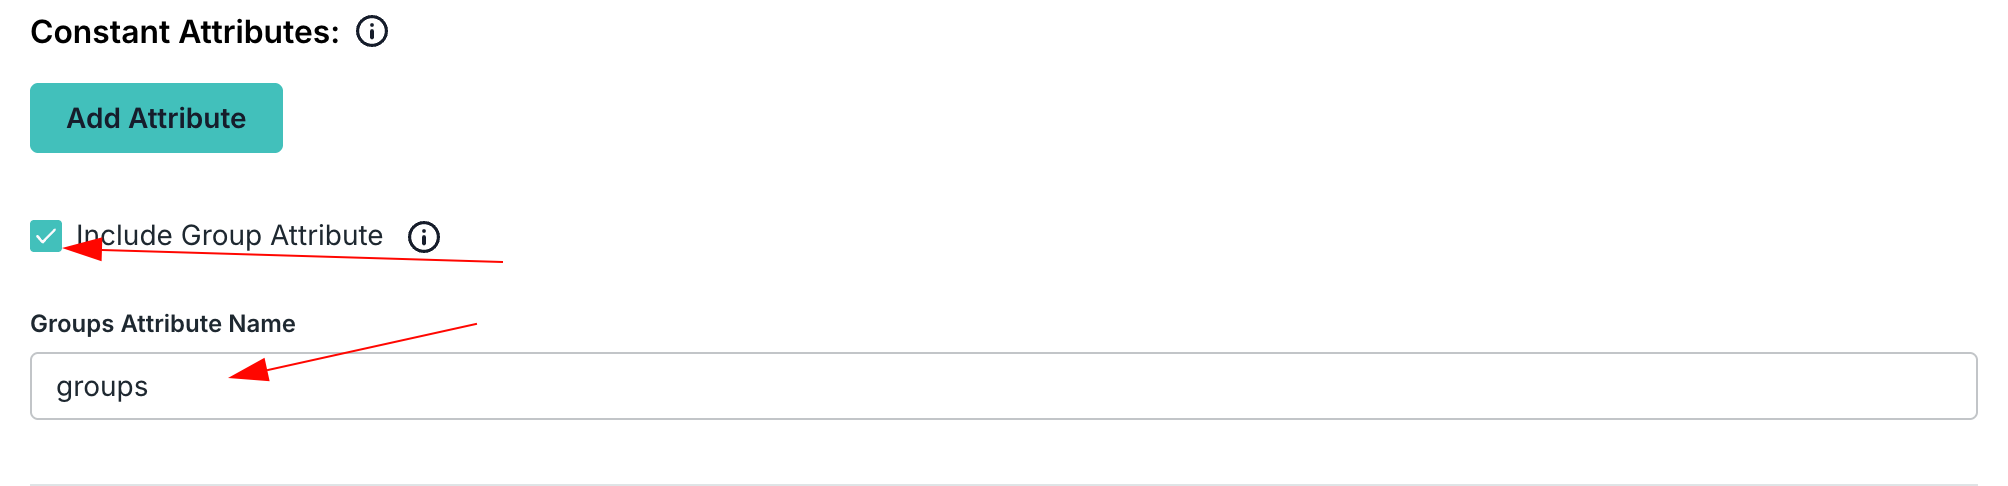
Under the Constant Attributes, set the following attributes:
Include Group Attribute—Keep the checkbox selected.
Groups Attribute Name—Type groups.
SSO role mapping uses the group names sent in the groups SAML attribute. The JumpCloud group name must match the corresponding Wasabi SSO role name.
Click Save.
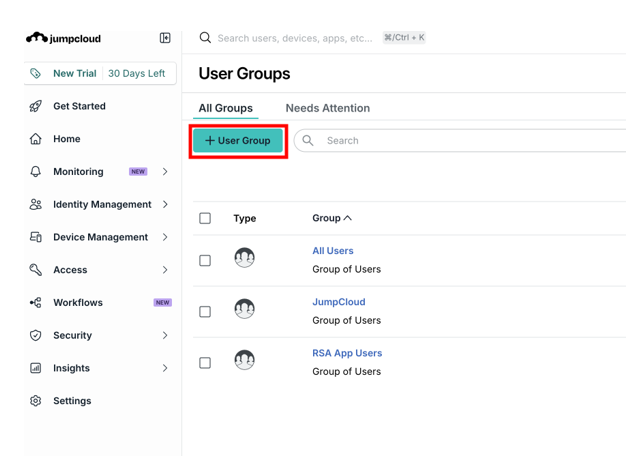
Select Identity Management from the navigation menu, then select User Groups. Create user groups based on your personal or company use case. User group settings depend on your organization's requirements.
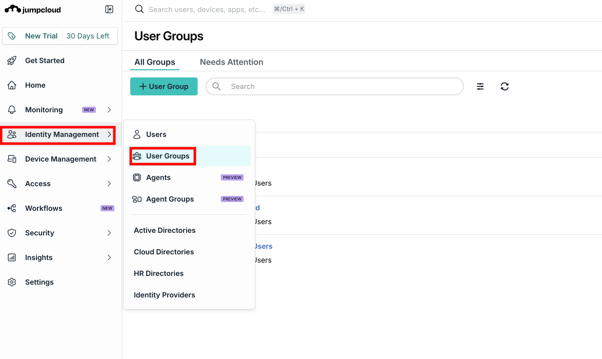
Click + User Group to add a new user group. The New User Group panel is displayed.
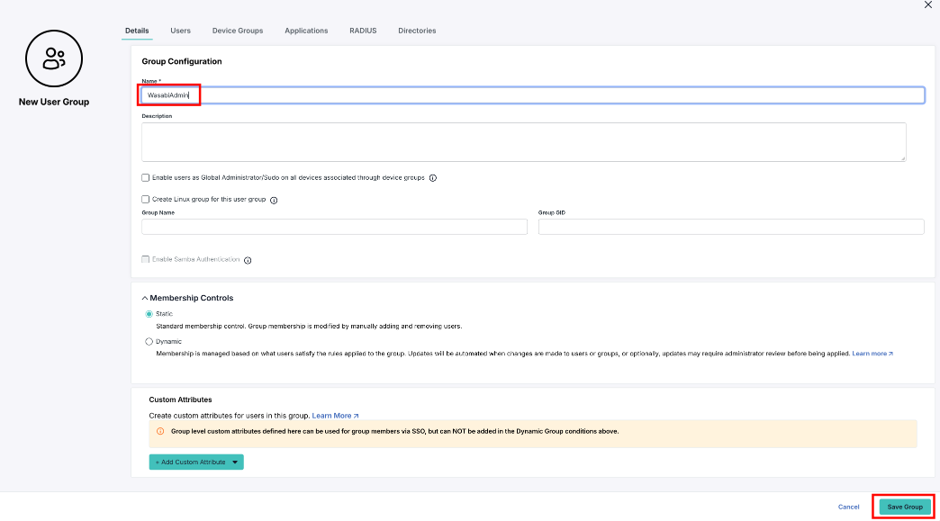
On the Details page in the Group Configuration section, enter a group name in the Name box (for example, WasabiAdmin), then click Save Group.
The group name must match the Wasabi role name in the Wasabi Console, you will create later in this procedure.
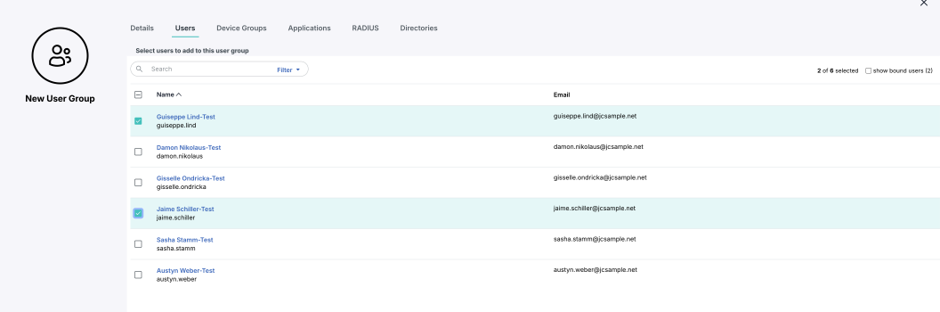
Select the Users tab, then select the checkboxes to add users to the group.
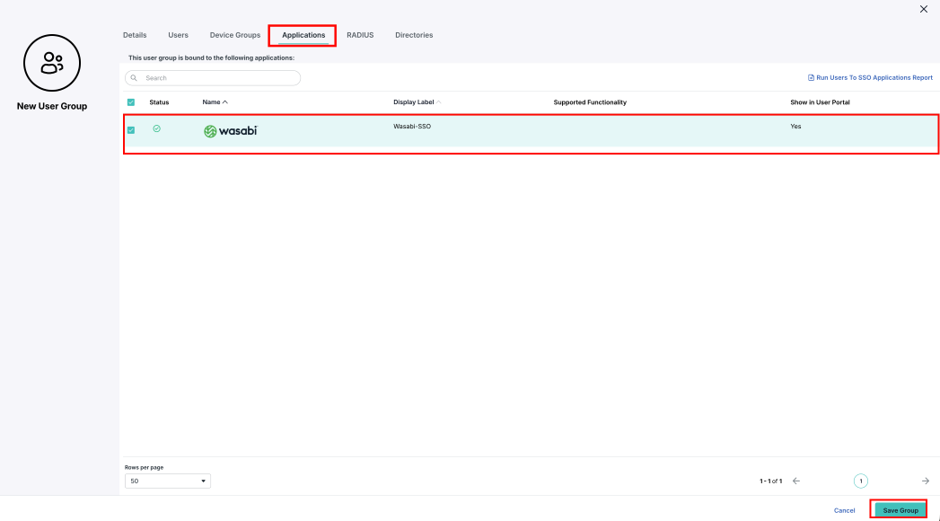
Select the Applications tab, then select the Wasabi application with the Display Label Wasabi-SSO using the checkbox. Click Save Group.
Download the IdP certificate. From the navigation menu, select Access, then SSO Applications, and then the previously created application.
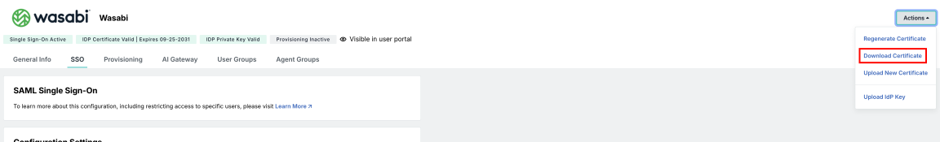
In the Applications panel, click Actions in the top-right corner, then select Download Certificate. The .pem file will be downloaded.
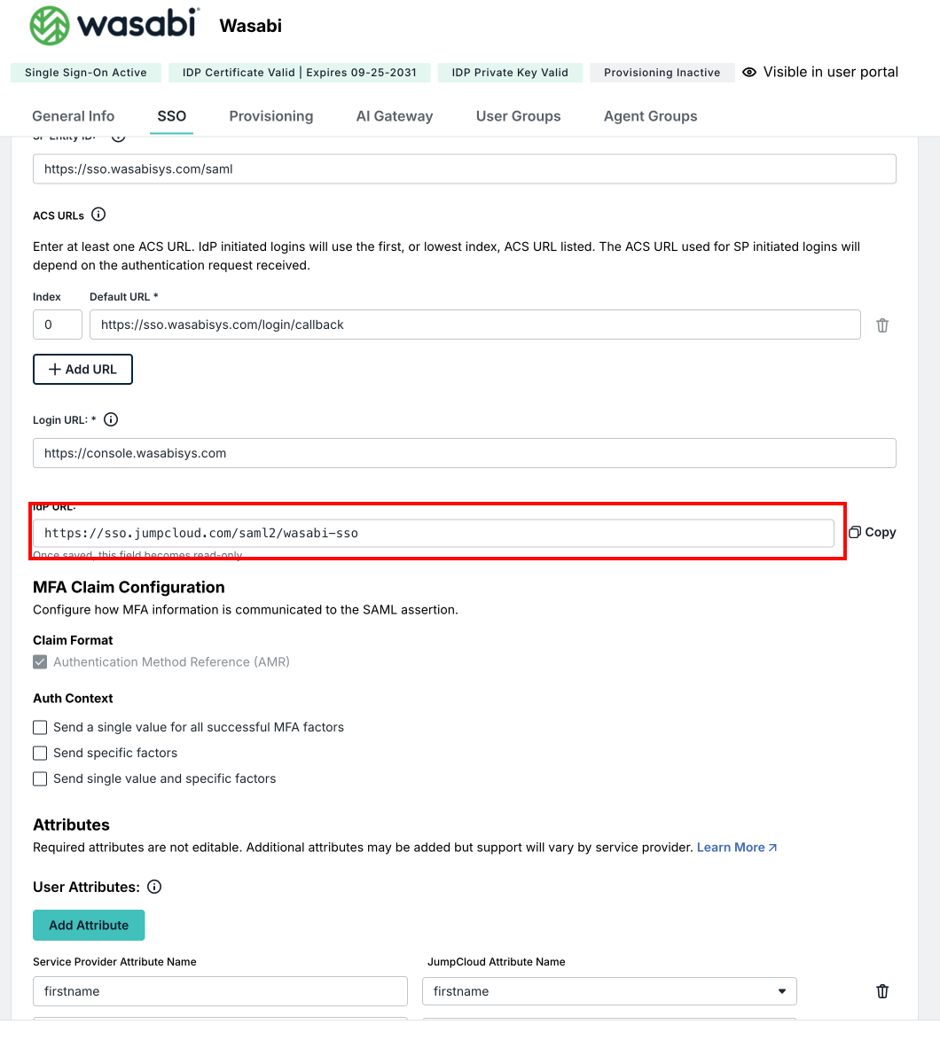
On the SSO page, scroll down to the IDP URL field and copy the URL.
Configuring SAML Settings in Wasabi Console (SP / Client)
Sign in to the Wasabi Console (https://console.wasabisys.com/login) using a Root account email. The Wasabi Management Console is displayed.
Click Security in the left menu, then select SSO (Single Sign-On) and configure the settings.
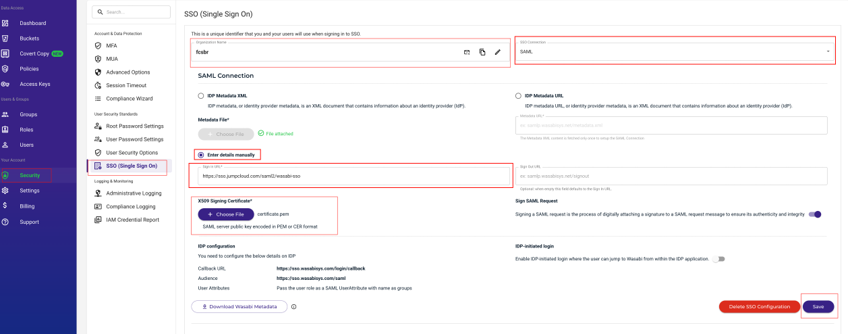
Configure the following settings:
Organization Name field—Type your organization's name (without spaces).
SSO Connection field—Select SAML from the dropdown.
SAML Connection, Enter Details Manually—Select this option.
Sign In URL field—Paste the previously copied URL.
X509 Signing Certificate field—Select Choose File and upload the IDP certificate (.pem) file.
Click Save.
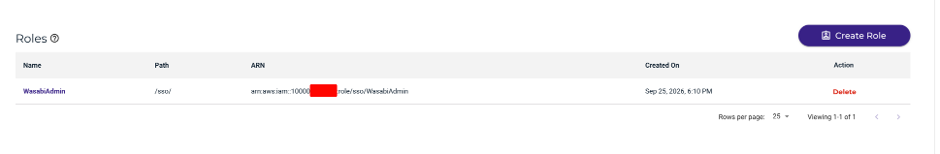
On the SSO page, click Create Role. The role is mapped to users through SAML claims sent by your organization’s Identity Provider (IdP). The role name in Wasabi must match the corresponding group name sent by the IdP.
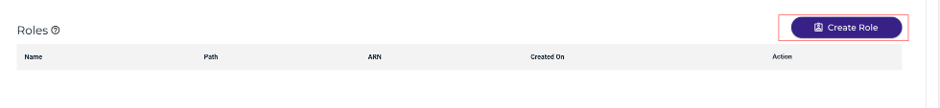
Do not create the role through the Roles tab in the left menu. SSO roles must be created through the SSO tab in Settings.
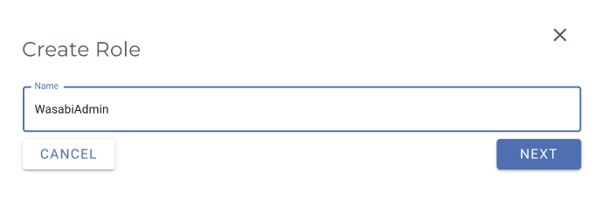
In the Create Role panel, enter the name you created on the JumpCloud Details tab (for example, WasabiAdmin), then click Next.
In the Assign Role Policies panel, select one or more policies to grant user-specific access to this new role, then click Create Role. For information on default policies or creating your own IAM policies for the Wasabi Console, see Policies in Wasabi Hot Cloud Storage.
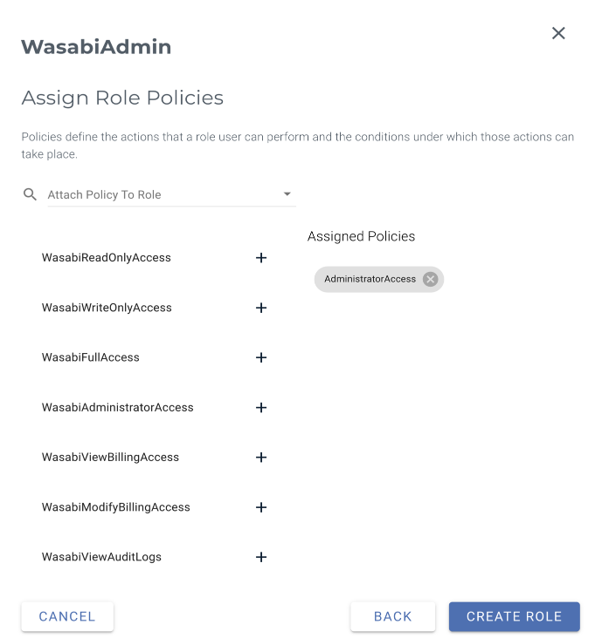
The role created in this example uses the AdministratorAccess policy. You can attach any Wasabi-managed or user-managed policy based on your access requirements.
Testing the Integration
Sign in to the Wasabi Console (https://console.wasabisys.com) with your credentials, then click Sign In with SSO to test the SSO configuration.
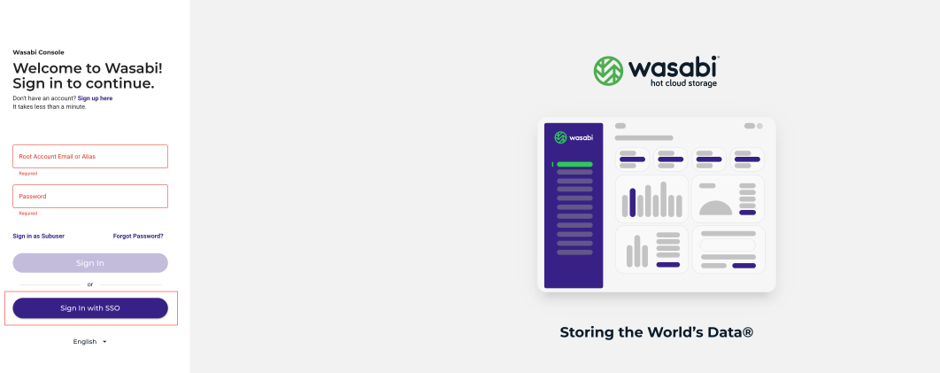
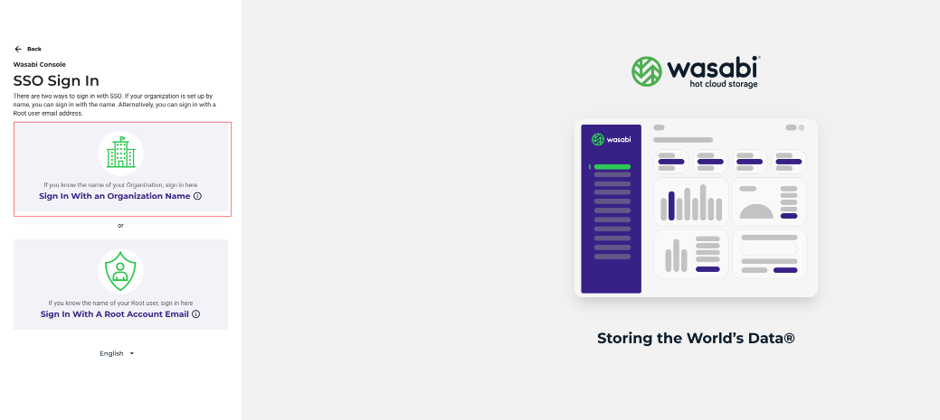
Click Sign In With an Organization Name. You are redirected to the Wasabi page that requests your Organization Name.
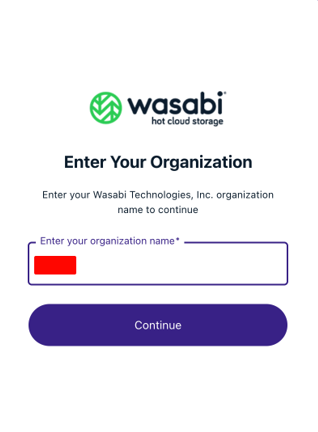
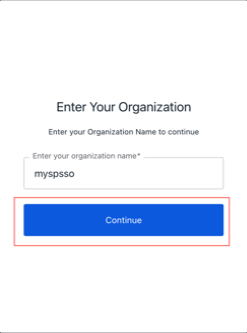
Enter your organization’s name, then click Continue. You will be redirected to the JumpCloud login page.
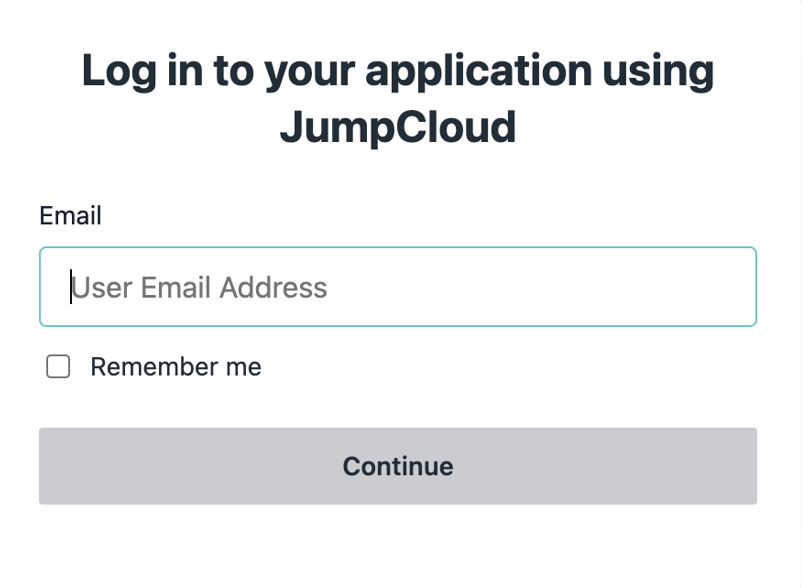
Enter your user email address, then click Continue. When prompted, type your password and click SSO Login.
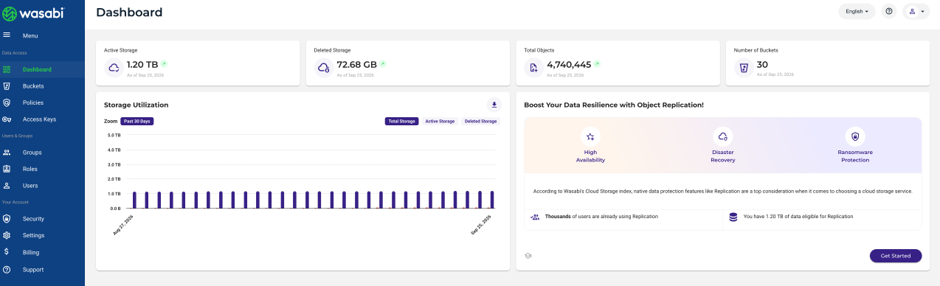
Once you have successfully logged in using your organization’s JumpCloud user email address and password, you are redirected to the Wasabi Console.
Your view of the Wasabi Console may differ from this example, depending on the IAM policy assigned to the SSO role you created.
Configuring WACM SSO With JumpCloud
This section outlines the steps to configure WACM SSO with JumpCloud using SAML application settings. Some steps from the Configuring SAML App in JumpCloud (IdP Side) section are repeated and referenced here for convenience.
Configure WACM SSO settings as described in step 5 of the Configuring SAML App in JumpCloud (IdP Side) section under SSO.
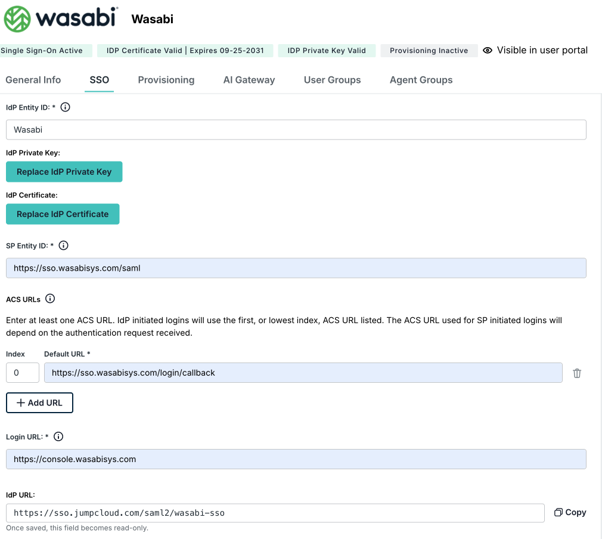
Use the following settings:
IdP Entity ID—Enter Wasabi (or any other name). The IdP entity ID is the unique, case-sensitive identifier that JumpCloud uses for this service provider. Be sure that the value you enter matches the Identity Provider entity ID you configured on the Wasabi Console SSO configuration page.
SP Entity ID—
https://wasabi-iam-prod-1.us.auth0.com/api/v2/ACS URL—
https://wasabi-iam-prod-1.us.auth0.com/login/callbackLogin URL—
https://auth.wasabisys.comIdP URL—Keep as is. Copy this information for use in the WACM configuration.
Scroll down to the Attributes section, then click Add Attribute to add the attributes as described in steps 6 to 9 of the Configuring SAML App in JumpCloud (IdP Side) section.
In the User Attributes section, click Add Attribute.
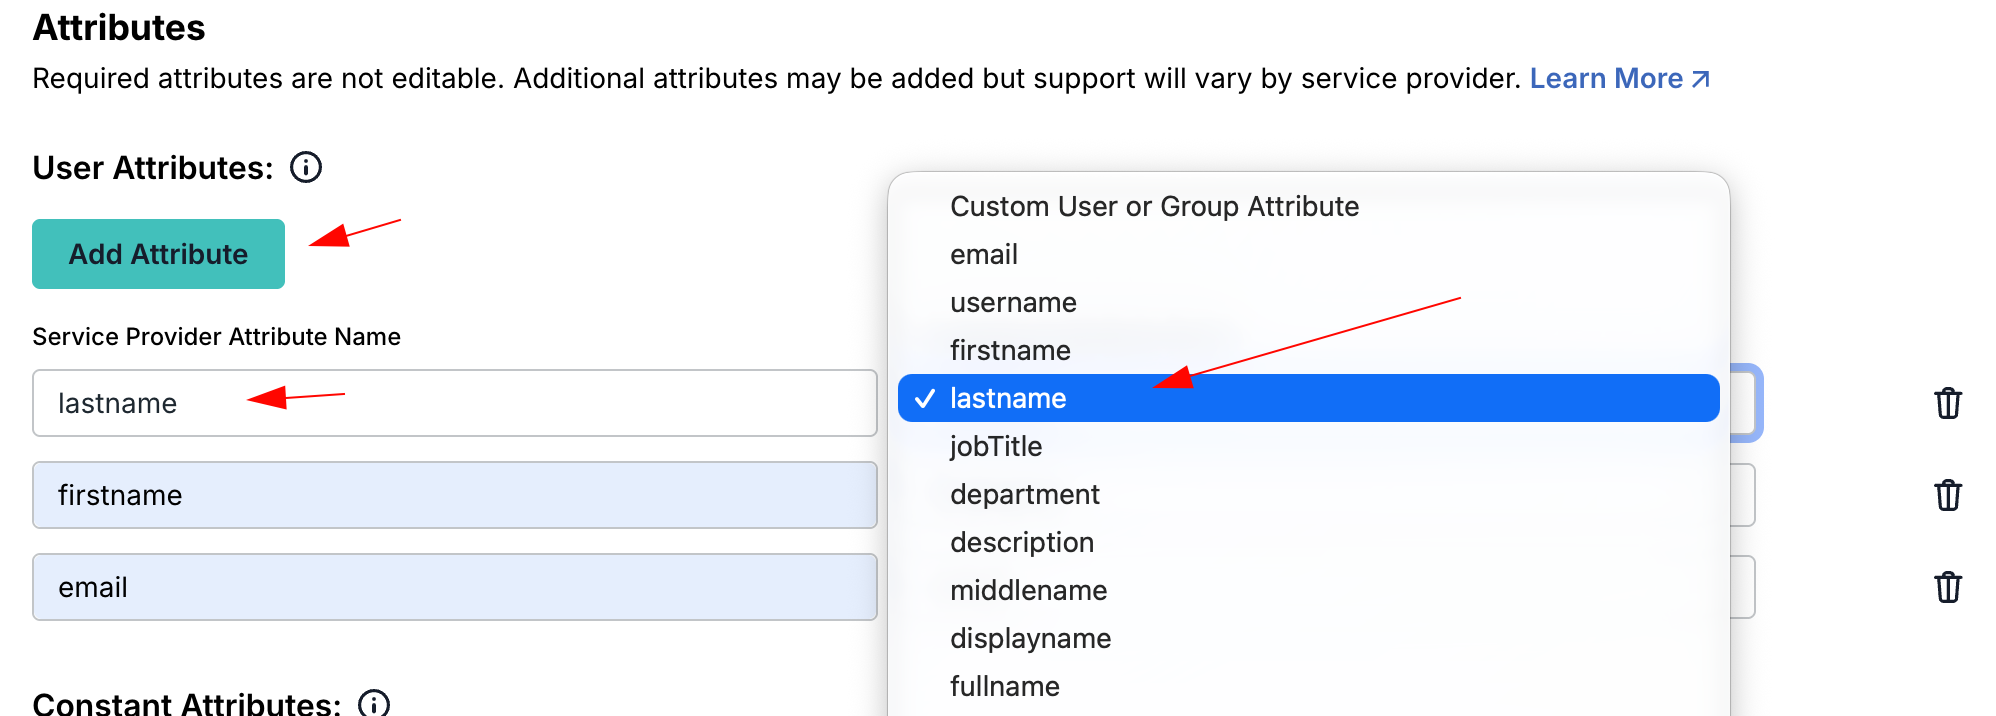
Under User Attributes, map the following attributes:
Service Provider Attribute Name—Type the attributes: lastname, firstname, and email in the corresponding fields.
JumpCloud Attribute Name—Select the same attributes from the dropdown menus: lastname, firstname, and email.
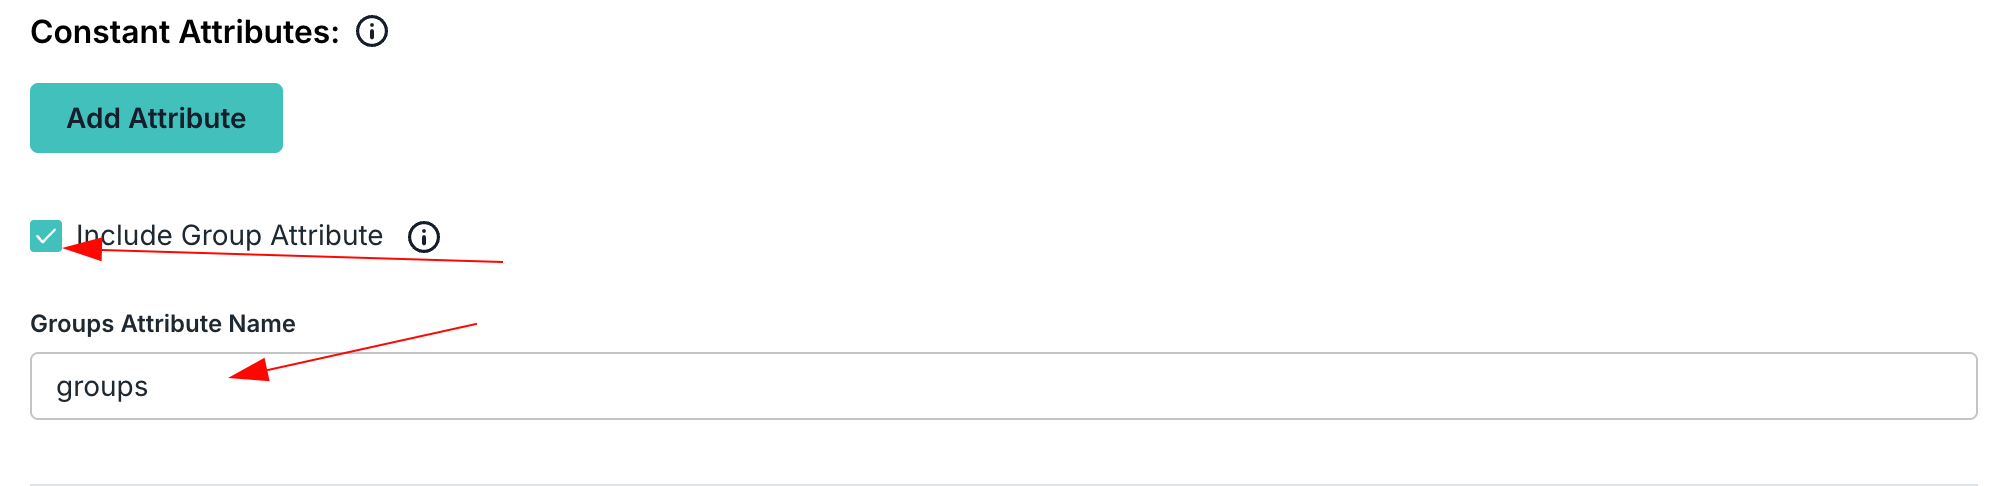
Under Constant Attributes, set the following attributes:
Include Group Attribute—Keep the checkbox selected.
Groups Attribute Name—Type groups.
Click Save.
Create User Groups for WACM roles as described in steps 10 through 14 of the Configuring SAML App in JumpCloud (IdP Side) section, under User Groups.
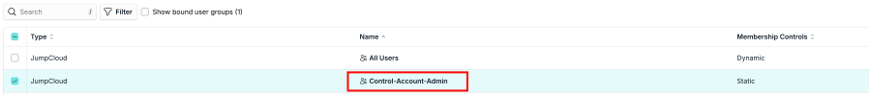
Create the four active user roles listed here, replacing spaces with dashes:
Control-Account-Admin
Control-Account-Staff
Control-Account-Staff-(Lite)
Control-Account-View
Download the IdP certificate as described in step 15 of the Configuring SAML App in JumpCloud (IdP Side) section.
Sign in to the WACM Console (https://wacm.wasabisys.com). In the top-right corner, select your user information, click My Profile, then select the Account tab.

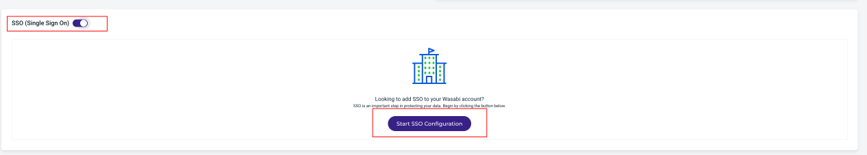
Scroll down to the SSO (Single Sign-On) section, enable the toggle, then click Start SSO Configuration.
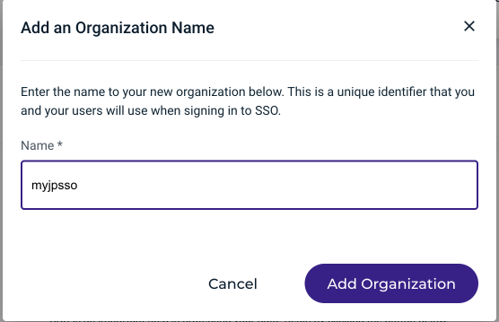
In the Add an Organization Name panel, enter your organization's name, then click Add Organization. (The organization name should be short and meaningful for user login.)
Configure SSO connection settings.
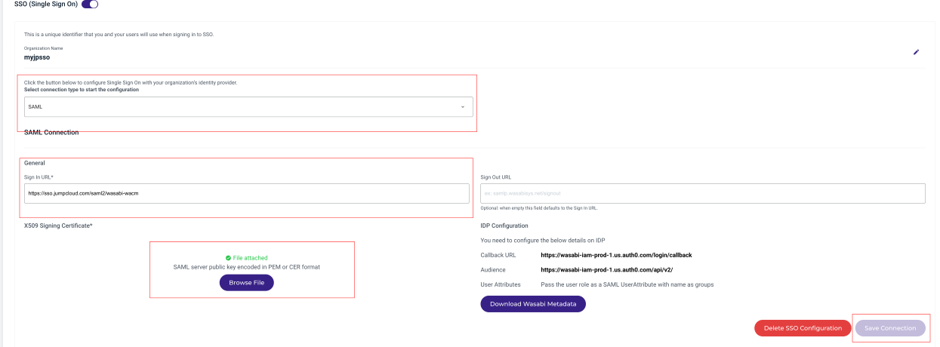
Use the following settings:
SAML Connection field, Select the connection type—Select SAML instead of OPEN ID.
General field, Sign In URL—Paste the IdP URL from JumpCloud.
General field, Sign Out URL—Leave this field blank.
X509 Signing Certificate—Select Browse File and upload the certificate you downloaded from JumpCloud.
Click Save Connection, and then log out. The Role section has already been populated.
To test the SSO login, sign in to the WACM Console (https://wacm.wasabisys.com) with your credentials, then click Sign In with SSO.
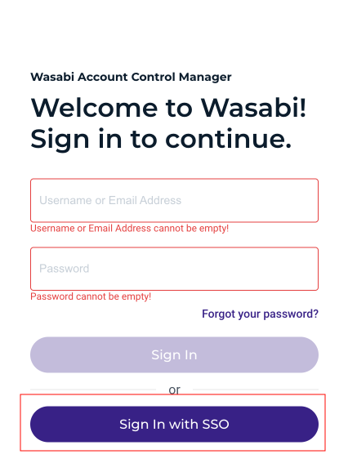
In the Enter Your Organization panel, enter the name created in the WACM SSO Configuration section, then click Continue. You are redirected to the JumpCloud login page.
On the JumpCloud login page, type your email and password, then click SSO Login.