FortiGate NGFWs deliver industry-leading enterprise security for any edge at any scale with full visibility and threat protection. FortiGate NGFWs now partner with Wasabi to extend visibility & monitoring. Follow the instructions below to integrate NGFWs with Wasabi.
Requirements
FortiOS v6.4.8 Build 1914 or higher recommended
Current FortiGuard subscription that provides current application signatures
Active Wasabi’s Hot Cloud Storage subscription
Reference Architecture
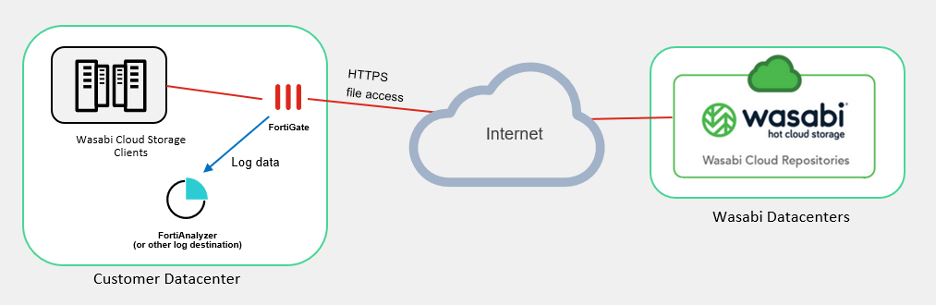
A FortiGate firewall must be in the data path between the Wasabi client and the Wasabi storage regions.
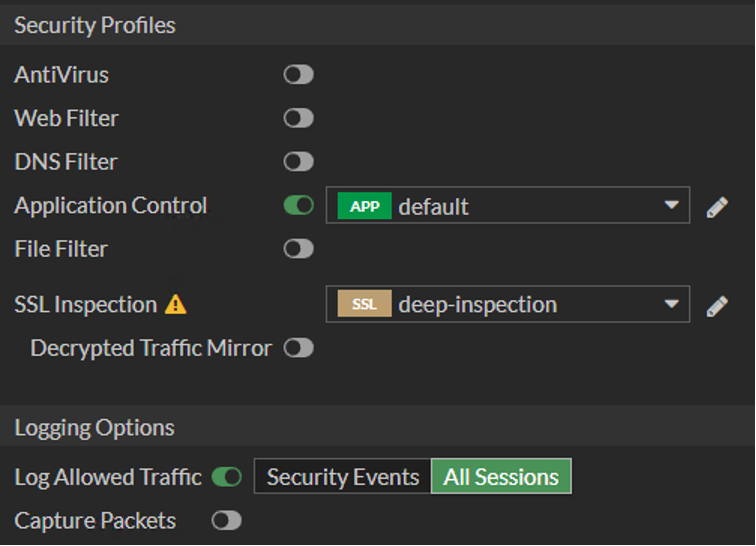
A firewall policy rule should exist with the following.
Permits the desired traffic from the client host to Wasabi
Enables the Application Control feature
Enable deep inspection for the SSL Inspection feature
Note: If deep inspection is disabled, FortiGate firewall will identify traffic being sent to/received from Wasabi. When enabled, Fortigate firewall will be able to detect what type of interactions are being exchanged with Wasabi storage upload, download, or deletion
Enable the Log Allowed Traffic with All Sessions option.
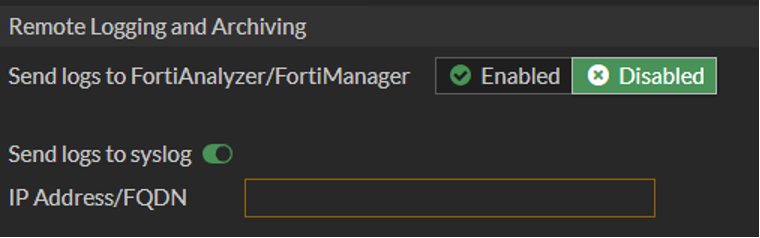
To use logging via syslog, go to Log Settings, Remote Logging and Archiving.
Enable the syslog option and enter the destination syslog IP.
Additionally, FortiAnalyzer can serve as a logging destination, with logs accessible via its API or forwarded to a packet capture infrastructure.